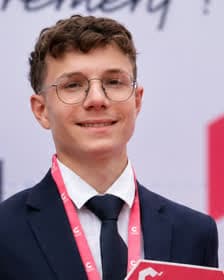
Téo Brondel
Founder of Validra · Product engineer
I'm a self-taught product engineer based between Chartres and Paris. I've spent about two and a half years building web products end to end, and shipped nine of them.
Validra started from what I kept seeing while building: the same security mistakes come back in almost every fast-shipped app. Row-Level Security that looks enabled but lets everyone read everything, private keys shipped to the browser, API routes that never check who is asking. I now review other teams' apps for exactly those failure modes.
What I build
- Portlio
Client onboarding for freelancers, with Stripe payments.
- EvacReport
B2B app for fire drill reports, built to work offline.
- MonBac
An interactive AI coach to practice for oral exams.
- Validra
Security reviews for SaaS and web apps.
Stack I work with every day: Next.js, React, TypeScript, Supabase, PostgreSQL, Stripe, webhooks and third-party APIs, LLM integrations.
How I review an app
- I start from how your product is supposed to work: who may see what, who may change what.
- I read the code when it's available, then test the running app with two separate accounts to check that data really stays isolated.
- Every finding I present as demonstrated is reproduced by hand, with evidence. Everything else is labeled as a weakness or an observation.
- I explain and prioritize; you or your developer implement the fixes, and I retest them.
What I don't do
- Certifications (SOC 2, ISO 27001) or legal compliance audits.
- Infrastructure or network penetration testing.
- Implementing fixes in your codebase.
Articles I've written
- RLS is On, But Your Supabase Data is Leaking: Detection & Safe Policies Guide
- OWASP Top 10 for Next.js & Supabase SaaS: Practical Audit Checklist (2026)
- SaaS Security Roadmap: The 90-Day Action Plan for Startups
- SaaS Security Audit Under €1,000: What Does a Real Review Cost in 2026?
- SaaS Security Checklist: 10 Technical Checks Every Founder Must Run Before Launch
- Securing Multi-Tenant SaaS: Complete Guide Against IDOR & RLS Leaks
- How to Answer SaaS Security Questionnaires and Pass Enterprise Vendor Due Diligence
- Manual Review vs Automated Scanners: Why Your SaaS Remains Exposed Despite Snyk or SonarQube